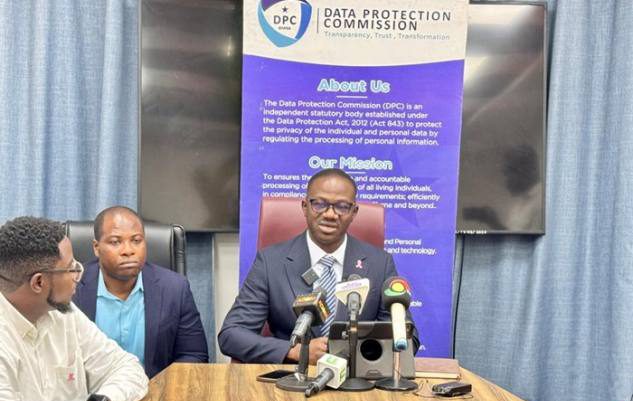
The Data Protection Commission (DPC) has referred a microfinance company and a health facility to the police for possible prosecution following inspections that uncovered breaches of data protection requirements.
The enforcement exercise, conducted in Accra on Monday, October 12, 2026, also revealed two hospitals operating with expired data protection certificates, while a third health facility had outstanding fees and other compliance deficiencies.
The exercise forms part of the Commission’s “year of enforcement” campaign aimed at ensuring that organisations comply with the Data Protection Act, 2012 (Act 843).
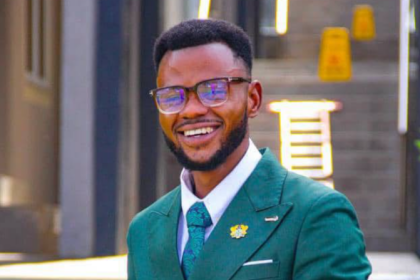
Speaking to the press, the Commission’s Executive Director, Dr Arnold Kavaarpuo, said the regulator would no longer depend solely on education and persuasion to compel institutions to meet their obligations.
He stressed that organisations must demonstrate compliance beyond merely obtaining registration certificates, particularly in how they collect, process, store and safeguard personal information.
Dr. Kavaarpuo disclosed that the Commission had recorded 2,575 data controller registrations in 2026, surpassing figures from previous years.
However, he insisted that the increase must translate into improved compliance and stronger protection of individuals’ information.
The Commission’s Director of Regulatory and Compliance, Mr Quintin Akrobotu, said the microfinance company had failed to renew its registration and complete a compliance report sent to it the previous year.
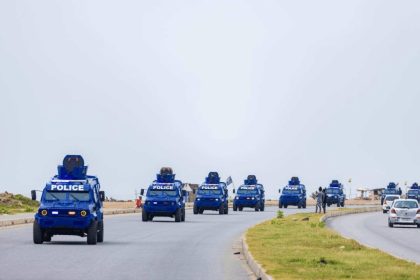
Its representatives were scheduled to report to the Criminal Investigations Department headquarters on Tuesday, October 13, for possible prosecution.
He said the clinic referred to the police had failed to appoint a Data Protection Supervisor and owed fees dating back to at least January 2025.
It had also not conducted a privacy impact assessment of its electronic health records system and lacked adequate technical and organisational safeguards.
The Commission warned that such lapses could expose sensitive personal information, including patients’ records, to misuse.
Dr. Kavaarpuo said processing personal data without the required registration could attract fines, imprisonment of up to two years, or both, upon summary conviction.
The enforcement exercise will continue into 2027, extending to other sectors, including religious institutions and the media.